

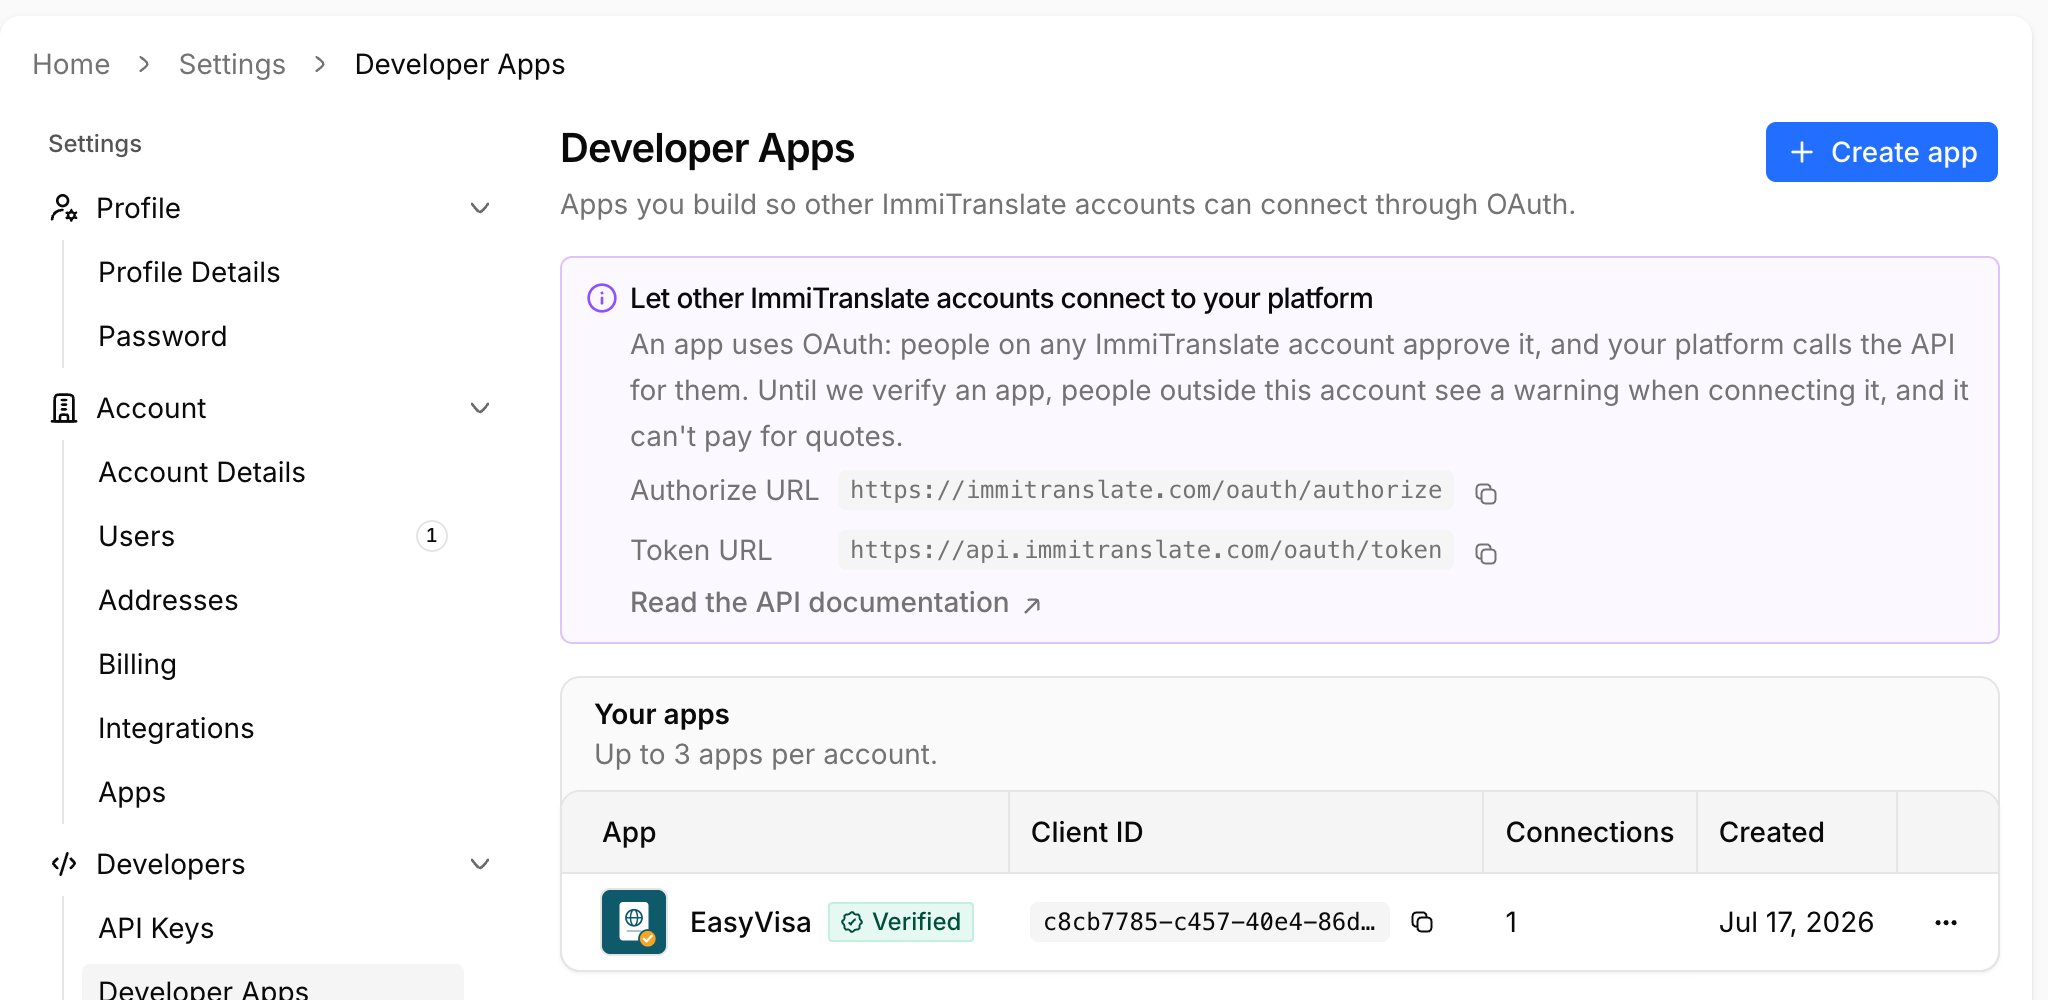
Settings → Developers → Developer Apps
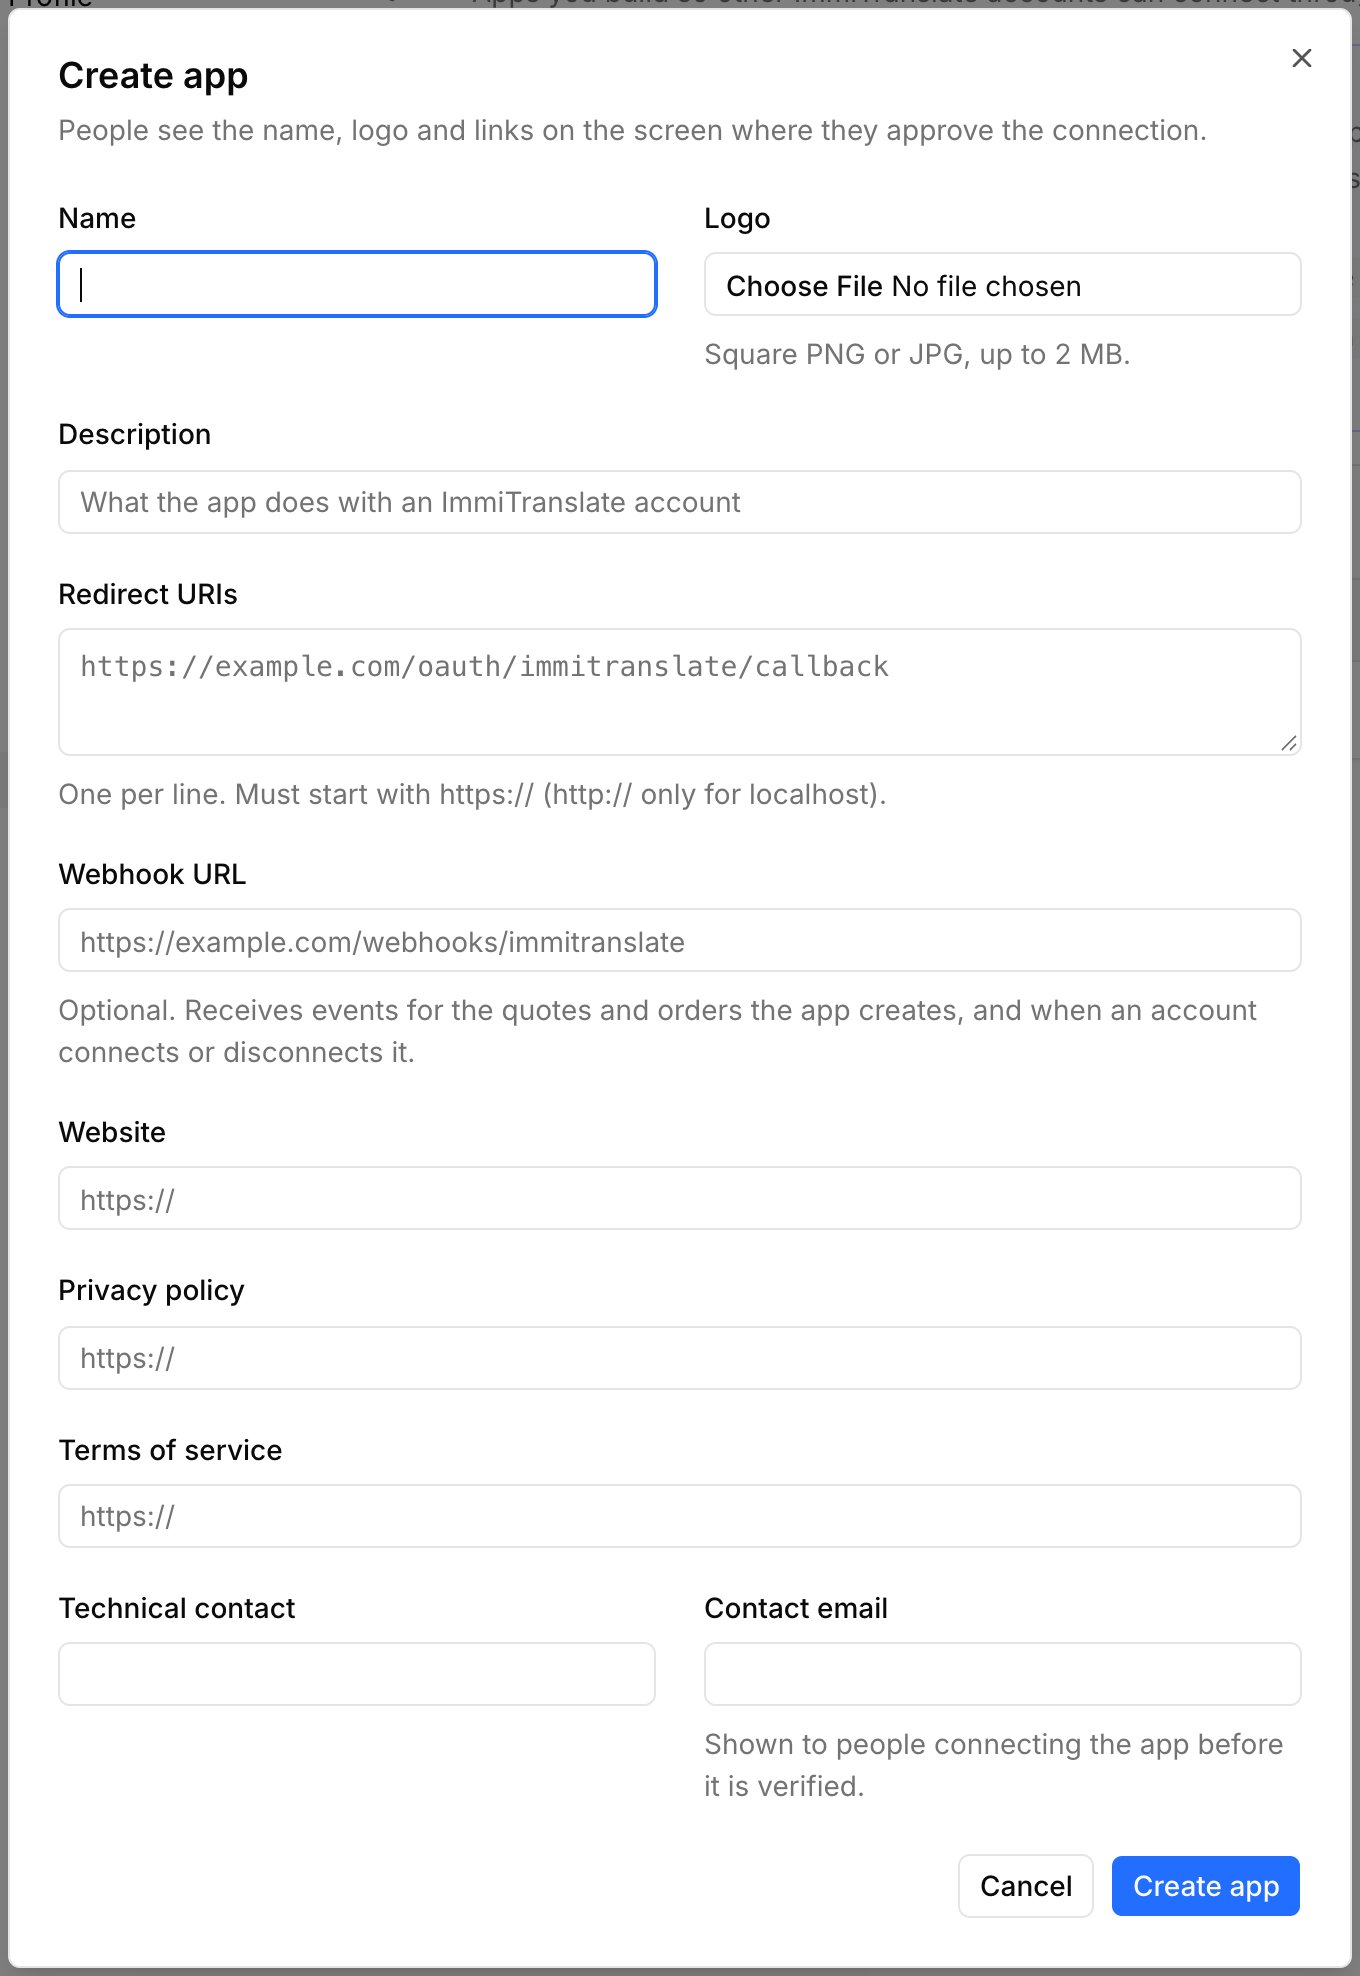
Creating an app. The name, logo and links appear on the screen where people approve the connection.
New apps are unverified: people outside your own account see a warning when connecting them, and they cannot pay for quotes. See Verification.
1. Send the user to ImmiTranslate
The user logs in or signs up, then approves the connection. If they have already connected your app, ImmiTranslate sends them straight back. An account can limit connecting apps to its admins; other users are told to ask an admin.
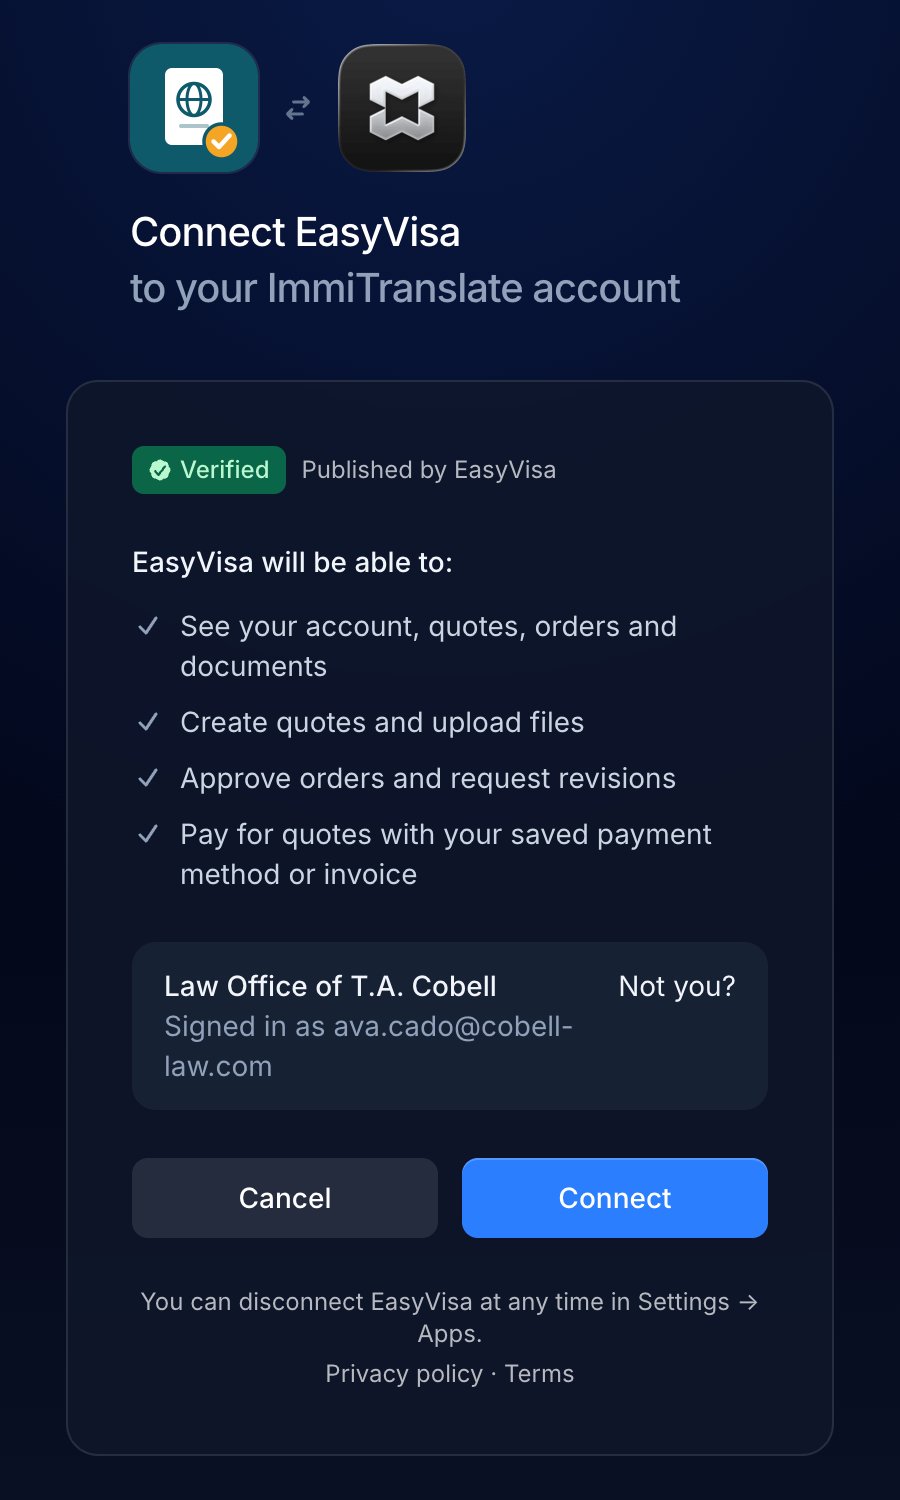
The approval screen for a verified app
2. Receive the code
ImmiTranslate redirects to yourredirect_uri with code and your state. If the user cancels, it redirects with error=access_denied instead.
3. Exchange the code for tokens
Authorization: Bearer ACCESS_TOKEN. Access tokens last 120 days. Before one expires, get a new pair with grant_type=refresh_token, your client ID and secret, and the refresh_token. Each refresh token works once and lasts 2 years.
To find out who connected your app, call Get Account: user is the person the token acts for, and app says whether your app is verified and can pay.
4. Disconnect
token_type_hint is optional. The connection is removed from the user’s ImmiTranslate account and every token your app holds for them stops working. The response is 200 with an empty body, even if the token was already revoked or unknown. A wrong client ID or secret returns 401 with invalid_client.
People can also disconnect your app themselves, under Settings → Apps in their ImmiTranslate account. You receive a connection / revoked webhook when they do.
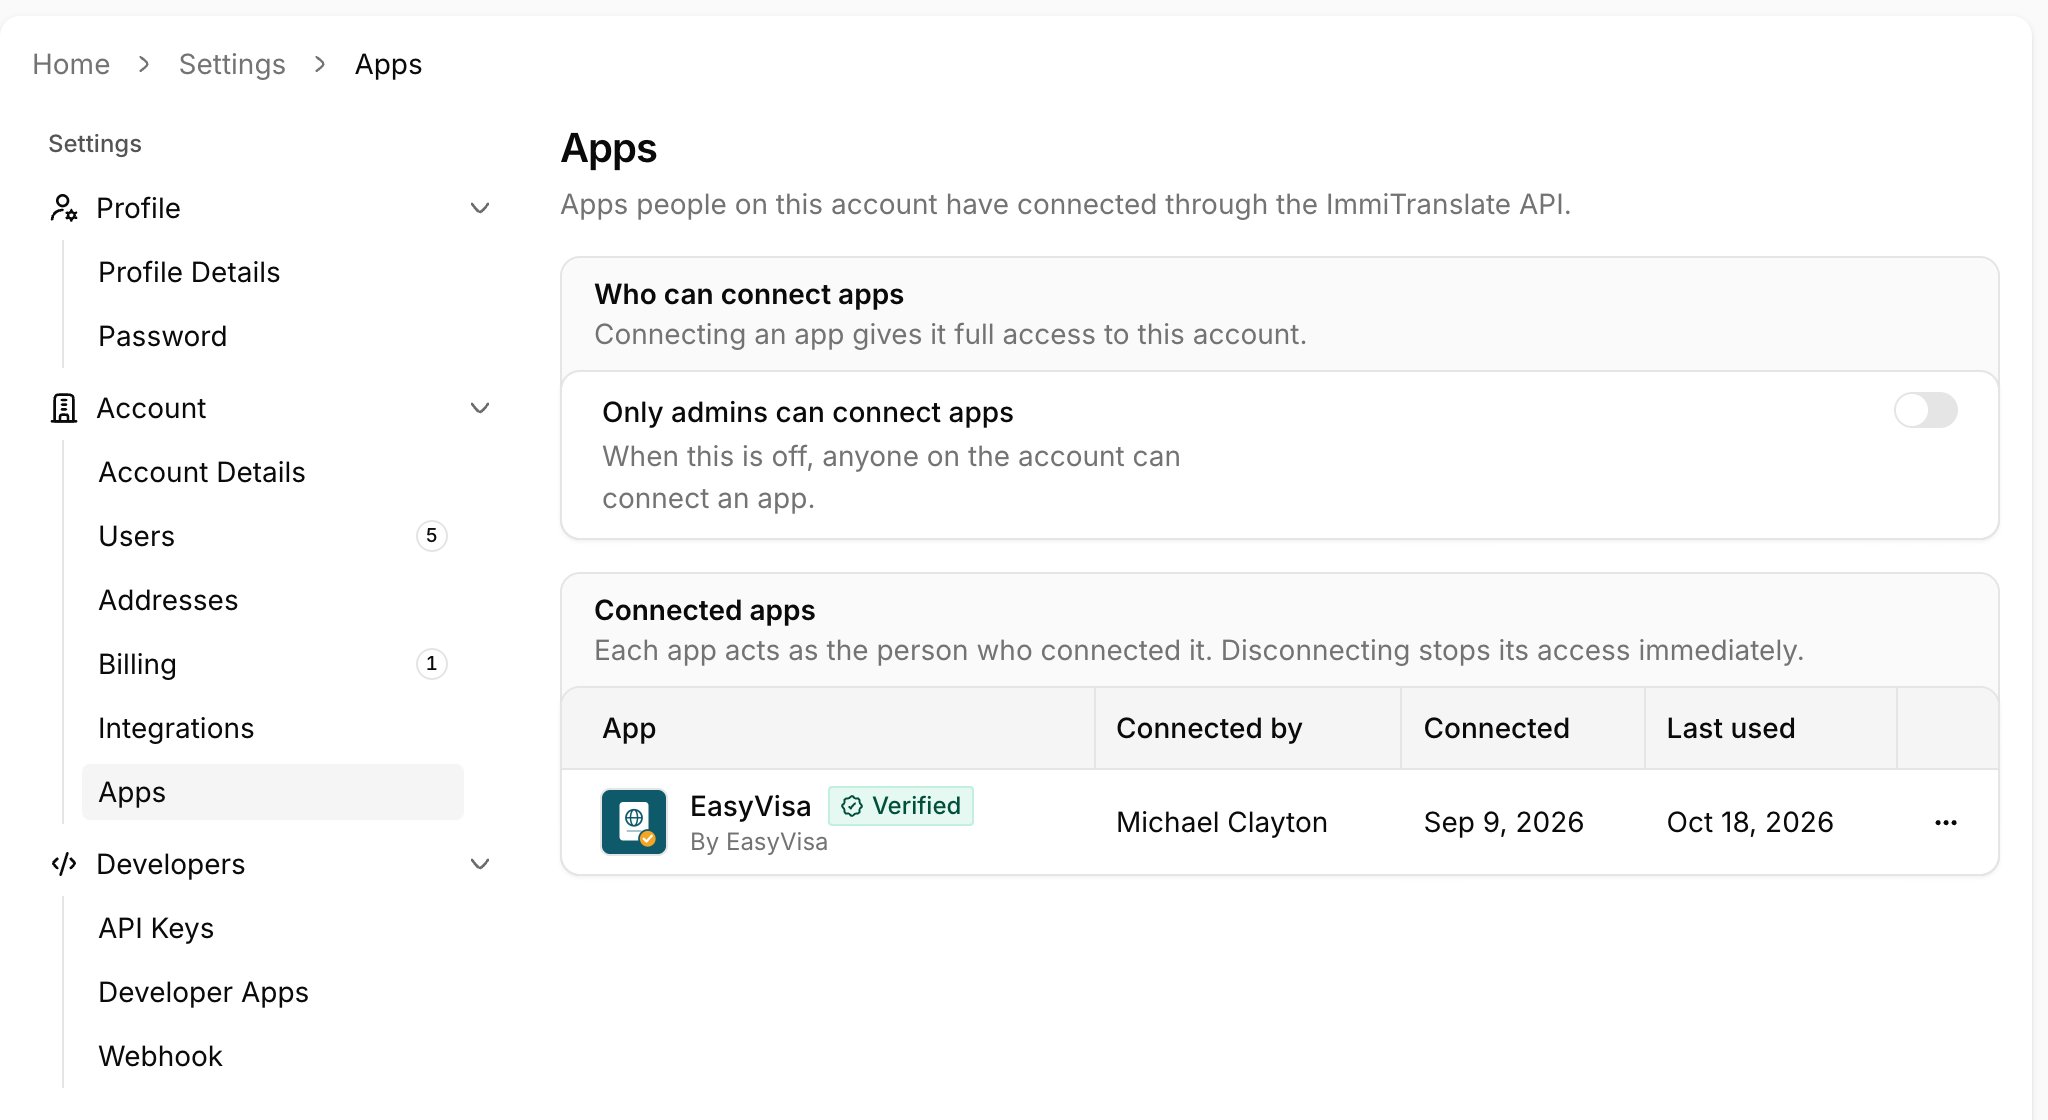
Settings → Apps in a connected account
Verification
New apps start unverified. Until your app is verified:- People outside your own account see a warning when they connect it.
- It can’t pay for quotes.
Pay Quote, andautobuyonCreate Quote, returnpayment_requires_verified_app.
Webhooks for apps
Set a webhook URL on your app on the Developer Apps page to receive webhook events for the quotes your app creates and the orders that follow, for every account connected to it, and for connections:connection/created— a user connected your app.targetis the account token;datahasaccount(token and name),user(token and email) andconnected_at.connection/revoked— the account disconnected your app in ImmiTranslate, with the samedataandrevoked_at. Not sent when your app revoked the token itself.
Webhook-App header with your app’s token and a Signature header: the hex HMAC-SHA256 of the raw request body, keyed with your app’s webhook signing secret (shown on the Developer Apps page). Compute it yourself and compare in constant time before trusting a delivery.